앞서 ModSecurity에 대해 간단히 다뤘다. 이번에는 우분투 컨테이너 생성부터 ModSecurity 구성과 테스트까지 진행했고 그 과정을 기록했다.
ModSecurity 구성
Ubuntu Container 설치(A)
A안에 앞서 다뤘던 Nginx Proxy Manager 구성
ModSecurity 설치
# 우분투 컨테이너 실행
docker run -it --name my-ubuntu-container ubuntu:latest /bin/bash

# NGINX Proxy Manager 설치
curl -fsSL https://deb.nodesource.com/setup_20.x | bash -

# apt install -y nodejs

# ModSecurity 설치
apt-cache search modsecurity
apt install libnginx-mod-http-modsecurity
apt install modsecurity-crs
apt install vim

ls /usr/share/modsecurity-crs/
`===========================================================
[실행결과]
owasp-crs.load  rules  uti
============================================================`

cat /usr/share/modsecurity-crs/owasp-crs.load

`===========================================================
[실행결과]
##
## This file loads OWASP CRS's rules when the package is installed
## It is Included by libapache2-mod-security2
##
Include /etc/modsecurity/crs/crs-setup.conf
IncludeOptional /etc/modsecurity/crs/REQUEST-900-EXCLUSION-RULES-BEFORE-CRS.conf
Include /usr/share/modsecurity-crs/rules/*.conf
IncludeOptional /etc/modsecurity/crs/RESPONSE-999-EXCLUSION-RULES-AFTER-CRS.conf
============================================================`
💬 Include 형태로 규칙이 들어있는 파일들이 지정되어 있는것을 확인할 수 있다.


# nginx 설치
apt install nginx

# nginx 실행
nginx
`============================================================
[실행결과]
nginx is running
=============================================================`

# nginx 프로세스 확인1
ps aux | grep nginx

# nginx 프로세스 확인2
service nginx status

# 80포트 리스닝 중인지 확인
ss -tuln | grep 80

# log 확인하기
tail -f /var/log/nginx/error.log
tail -f /var/log/nginx/access.log

# 다른 터미널에서 우분투 컨테이너 B 진입
docker exec -it my-ubuntu-container /bin/bash

# Nginx 상태 확인
curl -I http://localhost

# 우분투 컨테이너에서 accesslog 확인 -> 정상

# 컨테이너 시작시 Nginx가 포그라운드에서 사용될 수 있도록 하는 명령어들(아래 중 한가지 선택)
CMD ["nginx", "-g", "daemon off;"]
nginx -g 'daemon off;'
➡️ tail -f 명령어로 모니터링한 로그
127.0.0.1 - - [04/Jul/2024:23:45:31 +0900] "HEAD /?data=test HTTP/1.1" 403 0 "-" "curl/8.5.0"
127.0.0.1 - - [04/Jul/2024:23:45:55 +0900] "HEAD /?data=hello HTTP/1.1" 200 0 "-" "curl/8.5.0"
127.0.0.1 - - [04/Jul/2024:23:46:02 +0900] "GET /?data=test HTTP/1.1" 403 162 "-" "curl/8.5.0"
127.0.0.1 - - [04/Jul/2024:23:46:08 +0900] "GET /?data=hello HTTP/1.1" 200 615 "-" "curl/8.5.0"
tail -f 명령어로 모니터링한 로그
위와는 다르게 ModSecurity 로그 파일의 경로는 /etc/nginx/modsecurity.conf 파일 SecAuditLog 항목에서 확인할 수 있다.
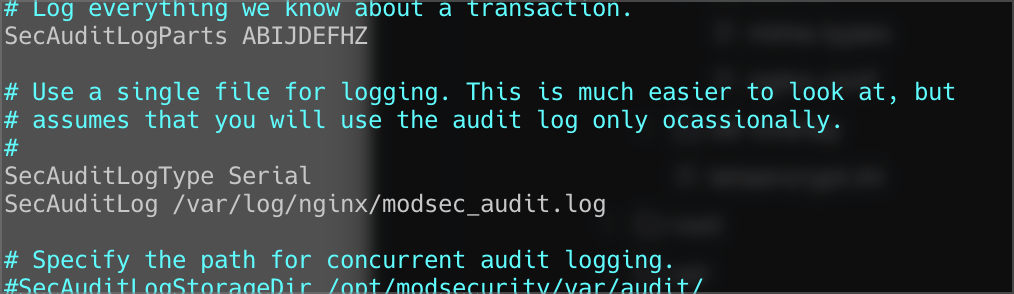
→ /var/log/nginx/modsec_audit.log 경로 확인완료
tail -f /var/log/nginx/modsec_audit.log 실행
보안 규칙에 위배되지 않는 request인 경우 아무런 로그가 확인되지 않다가, 위배되는 request 발생시 다음과 같은 로그가 확인된다.
---AU9HhbBg---A--
[04/Jul/2024:23:51:11 +0900] 172010467164.403561 127.0.0.1 57376 127.0.0.1 80
---AU9HhbBg---B--
HEAD /?data=test HTTP/1.1
Host: localhost
User-Agent: curl/8.5.0
Accept: */*

---AU9HhbBg---D--

---AU9HhbBg---F--
HTTP/1.1 403

---AU9HhbBg---H--
ModSecurity: Access denied with code 403 (phase 1). Matched "Operator `Contains' with parameter `test' against variable `ARGS:data' (Value: `test' ) [file "/etc/nginx/modsec/modsec_test.conf"] [line "1"] [id "1234"] [rev ""] [msg "param contains test"] [data ""] [severity "0"] [ver ""] [maturity "0"] [accuracy "0"] [hostname "127.0.0.1"] [uri "/"] [unique_id "172010467164.403561"] [ref "o0,4v12,4"]

---AU9HhbBg---I--

---AU9HhbBg---J--

---AU9HhbBg---Z--